Agentic Code Reviewer
Autonomous, context-aware code analysis agent that accelerates pull request workflows, spots subtle architectural debt, and enforces rigorous security standards before merge.
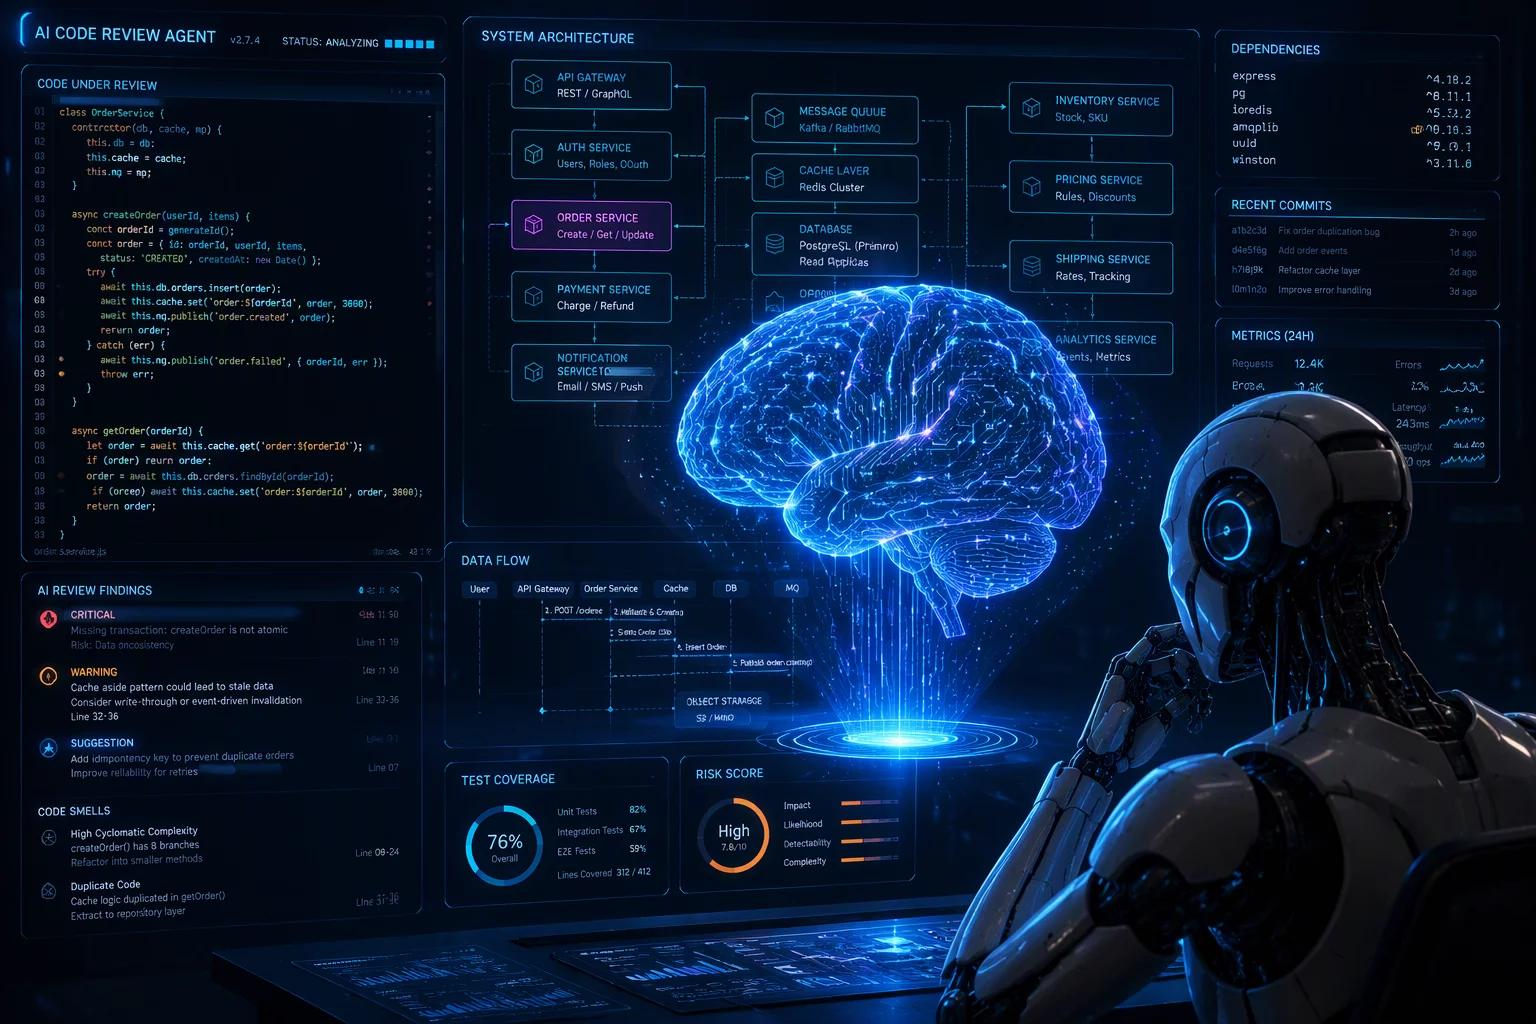
Zero-Latency PR Triage
Instant multi-file diff assessment and risk scoring.
Deep AST Analysis
Semantic syntax trees and memory leak detection.
Automated Policy Guard
Strict OWASP Top 10 and enterprise compliance checks.
24/7 Dedicated Support
Direct SLA access to architecture engineering specialists.
Autonomous Multi-Agent Static & Dynamic Code Intelligence
The Agentic Code Reviewer operates as an autonomous peer reviewer embedded directly inside your GitHub, GitLab, or Bitbucket repositories. Instead of relying on rigid linting rules or shallow heuristics, it runs isolated multi-agent reasoning loops that reconstruct full repository context, trace dependency trees, and simulate runtime implications of incoming pull requests.
Engineers receive structured inline commentary highlighting critical race conditions, architectural regressions, unauthorized credential leaks, and suggested refactoring diffs. The system operates on-premise or within your isolated virtual private cloud, guaranteeing complete code confidentiality without sending proprietary IP to public endpoints.
Key Solution Metrics
- Deployment Time:
- < 15 Minutes
- Architecture Level:
- L3 Agentic Reasoning
- API Throughput:
- 1,500+ PRs / Hour
- SLA Guarantee:
- 99.95% Availability
Perpetual enterprise license including full repository integrations, custom agent prompt modules, and 12 months of prioritized model updates.
- Native Git CLI, GitHub & GitLab CI/CD hooks
- Air-gapped on-premise or VPC cluster runtime
- Unlimited local repository analysis tokens
Comprehensive Architecture Specifications & FAQs
Every Agentic Code Reviewer package includes complete containerized microservices ready for Kubernetes or Docker deployment:
Context Graph Constructor
Builds a dynamic semantic map of your entire codebase, tracking cross-file dependencies and type hierarchies in real time.
Agentic Reasoning Engine
Coordinates specialized agents for security triage, algorithmic efficiency analysis, and code quality scoring.
Compliance & Security Sentinel
Detects hardcoded secrets, misconfigured permissions, memory leaks, and known CVE vulnerability signatures.
CI/CD Webhook & Bot Gateway
Posts actionable diff reviews, auto-generates test scenarios, and directly interfaces with automated merge gates.
| Supported Languages | Python, TypeScript, Go, Rust, Java, C/C++, C#, Kotlin, Swift |
|---|---|
| VCS Integrations | GitHub Enterprise, GitLab Self-Managed, Bitbucket Data Center, Azure DevOps |
| Infrastructure Footprint | 4 vCPU, 16 GB RAM minimum per 500 active developers (Kubernetes Helm chart included) |
| Security & Data Retention | Zero data egress; ephemeral in-memory processing; SOC2 & ISO 27001 compliant |
| Response Latency | Median 8.4 seconds for 1,000-line pull request reviews |
How does Agentic Code Reviewer handle confidential proprietary code?
The package runs fully within your private infrastructure. No code, metadata, or tokenized embeddings ever leave your VPC, ensuring total IP isolation and compliance with strict enterprise confidentiality standards.
Can we customize the review criteria to enforce internal style guides?
Yes. You can supply custom markdown guidelines, team-specific architectural rules, and severity thresholds via declarative YAML configuration files stored directly in your root repository.
How does this differ from traditional static analysis (SAST) tools?
Traditional SAST tools only check rigid patterns. The Agentic Code Reviewer understands contextual intent, detects complex multi-file logical bugs, writes suggested code fixes, and explains its reasoning in human terms.
Engineering Feedback
Leave Feedback
To leave a comment, please log in to your account.